Australian businesses are becoming increasingly dependent on digital technology. From managing customer information to processing online payments, companies use connected systems to support everyday operations. While these technologies improve efficiency, they can also introduce security weaknesses that remain unnoticed until an incident occurs.
For organisations looking to strengthen their security, penetration testing australia services offer a practical way to identify vulnerabilities before attackers exploit them. Rather than relying entirely on existing security software, businesses can examine how their systems respond to realistic cyberattack scenarios and address weaknesses that could affect their operations.
Why Cybersecurity Risks Increase as Businesses Expand
Business growth often involves introducing new software, hiring additional employees and expanding online services. Each development changes how information is accessed, stored and shared. Without regular security reviews, these changes may create vulnerabilities that businesses fail to recognise.
For example, a growing company might introduce a cloud-based customer management platform without reviewing user permissions. Former employees may retain access, or software updates may be delayed because teams are focused on other priorities. Such weaknesses can increase exposure to cyber threats.
What Does Penetration Testing Actually Involve?
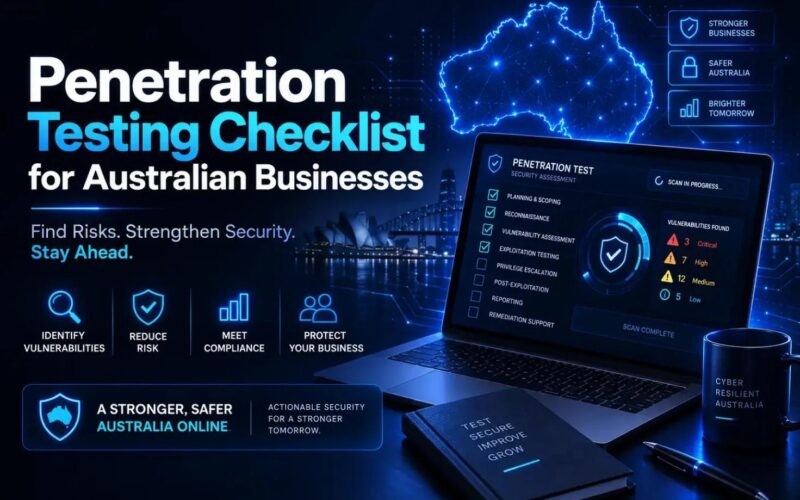
Penetration testing involves authorised security professionals assessing systems, networks or applications to identify exploitable vulnerabilities. Unlike basic automated scanning, it can include manual investigation to determine how weaknesses might be combined or exploited within agreed testing boundaries.
The assessment generally begins by establishing its scope and objectives. Security specialists then examine the selected environment, document their findings and explain the potential consequences. Businesses receive recommendations that help technical teams understand which problems require attention.
Testing does not guarantee complete protection against cyberattacks. However, it provides valuable information about existing weaknesses and supports more informed security decisions.
Common Security Weaknesses Businesses Should Address
Security problems can develop for several reasons, including outdated technology, configuration mistakes and inadequate access controls. Some vulnerabilities may appear minor individually but become more serious when combined with other weaknesses.
Common areas requiring attention include:
- Outdated software: Applications without current security patches may contain known vulnerabilities.
- Weak access controls: Excessive permissions can expose confidential business information.
- Insecure configurations: Incorrect system settings may create unnecessary opportunities for unauthorised access.
- Application vulnerabilities: Poorly protected web applications can place customer information at risk.
- Insufficient monitoring: Limited visibility can make suspicious activity harder to identify.
Recognising these issues allows organisations to prioritise improvements according to their business environment.
Why Australian Businesses Need a Proactive Approach
Cyber incidents can create financial and operational difficulties for organisations of different sizes. Disrupted services, recovery expenses and damaged customer relationships may affect a company’s ability to operate effectively.
Australian businesses must also consider relevant legal and contractual responsibilities when handling sensitive information. Depending on their circumstances, obligations under the Privacy Act 1988 and other applicable requirements may influence how personal information is protected.
A proactive approach helps organisations identify security weaknesses before they develop into larger problems. It also encourages management teams to consider cybersecurity alongside financial planning, operational continuity and customer service.
How Often Should Businesses Arrange Security Testing?
There is no single testing schedule suitable for every organisation. The appropriate frequency depends on business activities, technology changes, risk exposure and applicable compliance requirements. Budgeting also matters. Businesses can review guidance on Penetration Testing Cost when planning the scope and frequency of assessments.
Businesses should consider additional testing after introducing important applications, migrating systems to the cloud or making significant infrastructure changes. Customer-facing platforms and systems containing sensitive information may require more frequent attention.
Regular assessments are most effective when combined with vulnerability management, secure configurations, employee awareness and ongoing monitoring. Together, these measures support a more consistent approach to digital security.
Turning Security Findings Into Practical Improvements
The value of penetration testing depends on what happens after vulnerabilities are discovered. A technical report alone cannot improve security unless the organisation reviews its findings and takes appropriate action.
IT teams should prioritise vulnerabilities according to their severity, exploitability and potential business impact. Clear responsibilities and realistic remediation deadlines help ensure that important weaknesses are addressed.
Retesting significant fixes can confirm whether corrective actions have worked. Maintaining records of improvements also allows businesses to monitor their progress and identify recurring security problems.
Conclusion
Regular security assessments help Australian businesses understand their digital risks and make informed decisions about protecting important systems. As organisations expand, identifying vulnerabilities, improving access controls and maintaining secure technology become essential responsibilities.
Businesses seeking professional cybersecurity assessment services can explore cyberforte.com.au for support with penetration testing and security improvements. A consistent, proactive approach can help organisations strengthen their defences while continuing to grow with greater confidence.